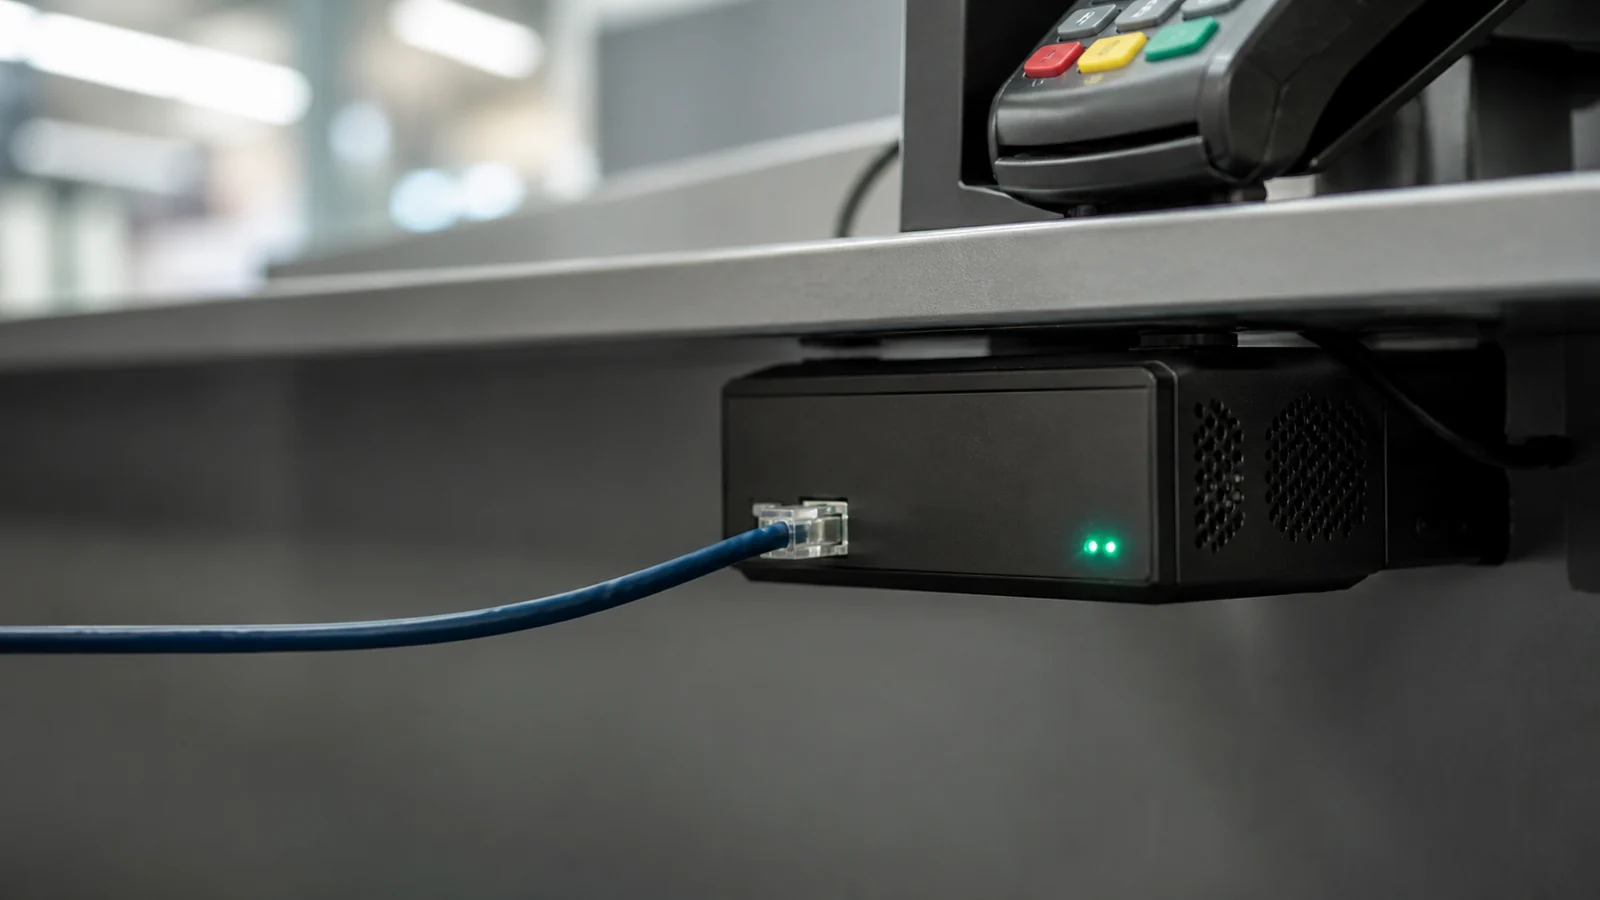
BREEZE COMET Hijacks Brazilian Payment Systems for Fraud
Mandiant traced BREEZE COMET from vishing, rogue branch hardware and stolen cloud credentials to payment APIs used for hundreds of fraudulent transfers.
Read article →Authentication, access, credentials, and identity systems.
Mandiant traced BREEZE COMET from vishing, rogue branch hardware and stolen cloud credentials to payment APIs used for hundreds of fraudulent transfers.
Read article →An exposed server revealed a repeatable Active Directory attack path, AI-assisted planning, Aurora lockers, and payment trails across multiple victims.
Read article →A new Windows loader arrives through a fake Teams help desk; modules sent to Expel’s emulator phish passwords and tunnel into internal services.
Read article →Two exploited miniOrange SAML flaws can mint WordPress admin sessions. Seven independently versioned editions make ordinary update and vulnerability checks unreliable.
Read article →The browser extension exposed vault tokens to untrusted page messages. Version 3.49.6 adds origin, frame, and nonce checks; later builds supersede it.
Read article →Unit 42 says stolen AI API keys can reach gray-market proxy services within minutes, turning one exposed credential into catastrophic usage charges.
Read article →Public research turns a patched NetScaler memory overflow into a root-code-execution risk for SAML deployments, making build verification urgent.
Read article →Customer contact data is public after a social-engineering breach; defenders should harden support and identity checks against targeted impersonation.
Read article →Rapid7 joined a SharePoint identity bypass to unsafe .NET type creation. August's cumulative updates complete Microsoft's two-cycle fix.
Read article →Government agencies traced Gunra from exploited edge devices through credential theft, cloud exfiltration, backup deletion, and cross-platform ransomware.
Read article →Remus uses an Ethereum smart contract to resolve changing command infrastructure before stealing browser sessions, credentials, and wallet data.
Read article →Code in a signed-in Windows session can invoke a TPM-backed Windows Hello for Business key, authenticate without a device identity claim, and create a path to durable Entra access.
Read article →SpecterOps shows how relayed WSUS machine-account access can forge targeted updates and bypass payload signature checks when SUSDB runs on a separate SQL Server.
Read article →Showing 92–104 of 112