Cloudflare Blocks PHP Exploits, Flags a Custom Upload-Field Gap
Cloudflare combines request and origin-response signals for PHP2Shell. One related WAF rule covers the default upload-progress field; operators still need PHP updates.
Read article →Software vulnerabilities, dependencies, and application security.
Cloudflare combines request and origin-response signals for PHP2Shell. One related WAF rule covers the default upload-progress field; operators still need PHP updates.
Read article →The dangerous-file upload issue requires a victim to follow a crafted link or interact with a compromised page. Compare installed Commerce, Magento, B2B and Events releases with Adobe's July updates.
Read article →Attackers are targeting exposed PAN-OS management interfaces. Restrict web UI and XML API access, then match each installed build to its hotfix.
Read article →With a known chain code, a compromised leaf signer share can lead back to the same party’s root share. Keep chain codes confidential while a library fix is pending.
Read article →A short TCP message can make older vsomeip endpoints allocate gigabytes. Upgrade to 3.7.4 or set a reliable message-size limit, then check memory and connection logs.
Read article →A new two-sided inventory links Claude Code and Codex plugin installations to repository publishers, enablement, components and observed source.
Read article →Affected firewalls need Brotli inspection and dataplane TLS decryption. Check the setting, disable inspection while hotfixes are pending, and verify the result.
Read article →FortiOS remains under investigation. Node.js has patched Brotli memory corruption and nine other flaws in the 22.x, 24.x and 26.x lines.
Read article →Malformed compressed input can overflow an eight-byte decoder buffer. Trace untrusted decompression paths and deploy fixed Node.js builds.
Read article →The 1.107.0 image provenance named a hyphenated source owner; startup files in that revision matched a poisoned PyPI wheel. Compare release inputs with shipped bytes.
Read article →Unit 42 observed access to password hashes and MFA secrets after PHP exploitation. Patch the serving workers, then hunt their child processes and investigate credential access.
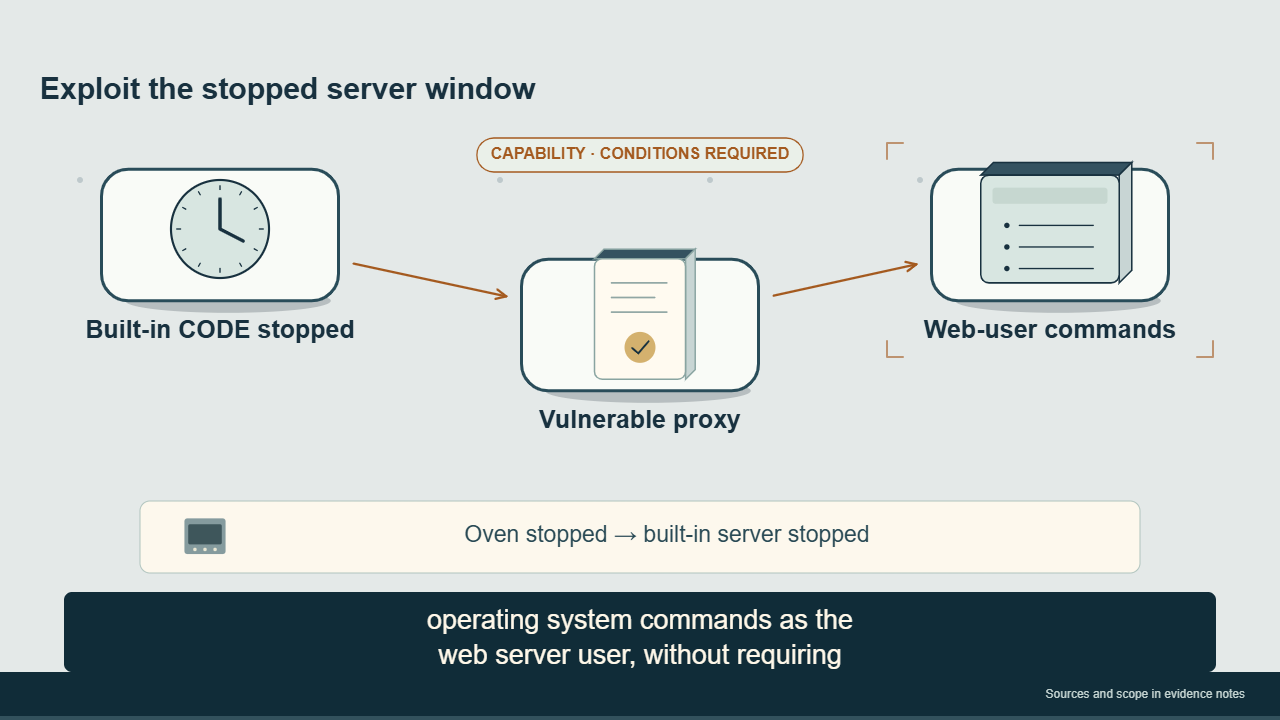
Read article →The richdocumentscode proxy exposes command execution while its CODE server is down. Update to 26.4.303 or remove the app, then look for web shells.
Read article →PHP patched two request-processing flaws, then warned of another rare code-execution path. Check the serving build and the upload-progress setting in every worker.
Read article →Showing 40–52 of 145