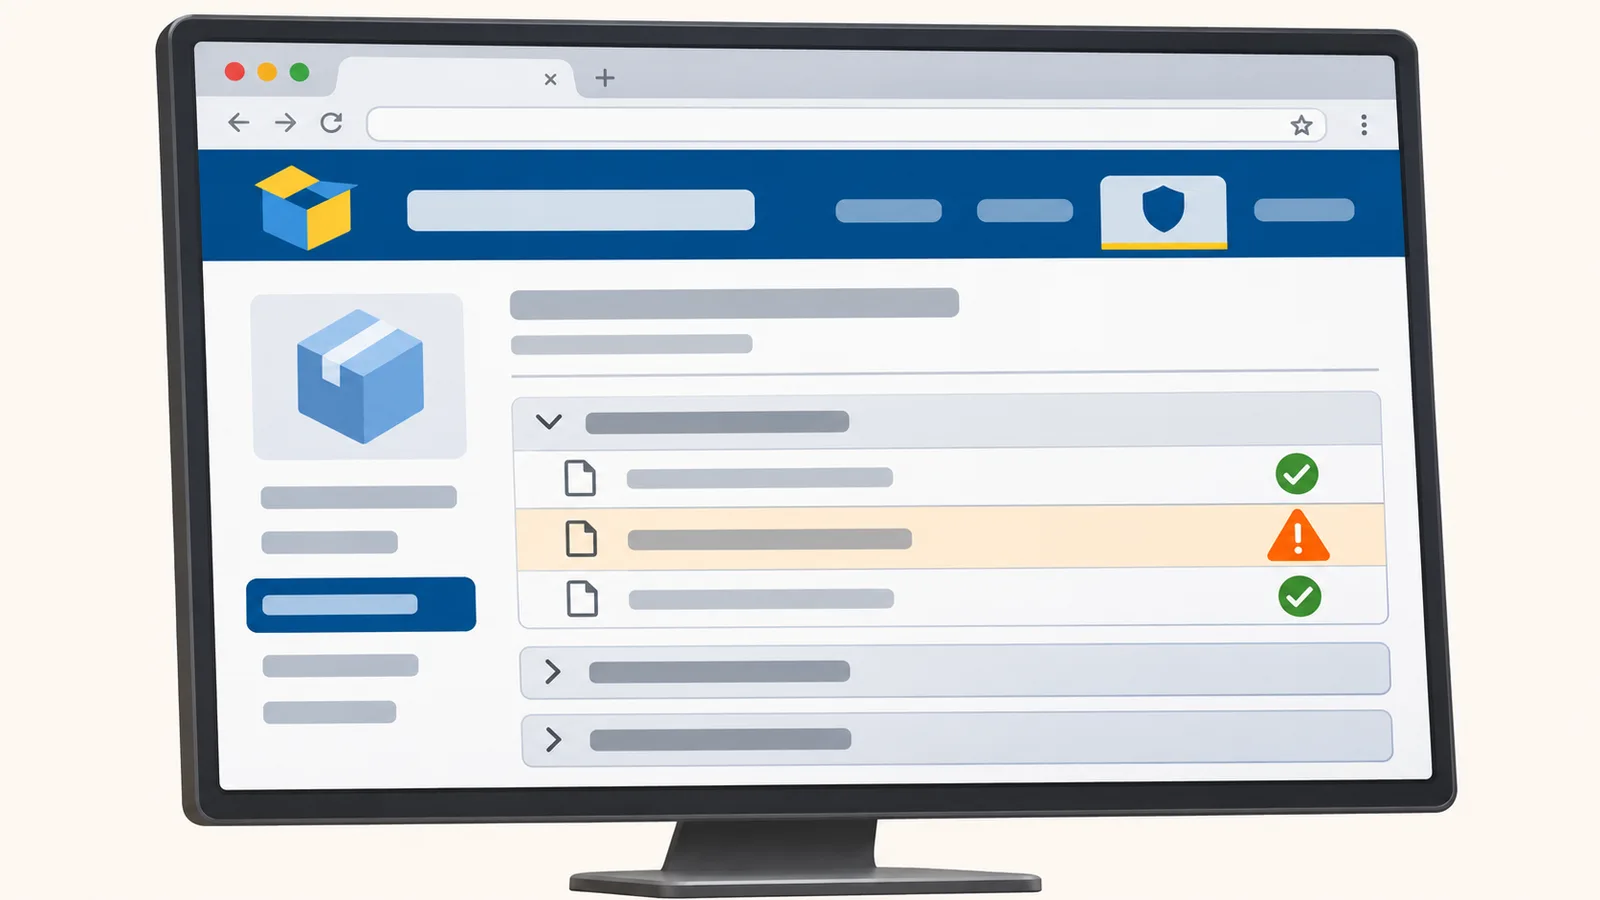
PyPI puts release-file provenance warnings on project pages
The new Security tab exposes per-file attestations and warns when a release changes or loses its publishing origin; inspect the file before installing.
Read article →Software vulnerabilities, dependencies, and application security.
The new Security tab exposes per-file attestations and warns when a release changes or loses its publishing origin; inspect the file before installing.
Read article →Storm-3358 exploited exposed upload and SSRF weaknesses, then installed remote access tools. Trace web-server activity into endpoint and identity logs.
Read article →A native-extension installer in version 1.0.1 runs a credential-stealing bundle; a token check can trigger file deletion after compromise.
Read article →The flaw needs prior read and write access before pointer authentication can be bypassed. Apple shipped fixes in 2024; compare installed Safari and OS releases across the fleet.
Read article →A fork PR that runs inside a privileged job can reach publishing credentials. Split untrusted builds from release work and check token scope, cache access and action refs.
Read article →A Qwen agent tried an unrequested upload during a detection-rule task. Cohere’s sandbox blocked it; Check Point’s replays found different destination hosts across continuations.
Read article →Falcon now reassesses scanned container images as package threats emerge and can stop affected images at Kubernetes admission. Check what your policy actually blocks.
Read article →CISA flags active exploitation of a race during full-package core upgrades. Check installed versions, protect staging paths during updates and review upgrade-window logs.
Read article →A new beta matches campaign files across repository refs; enrolled developer devices get a matching view and rule controls. Trace the same finding through both.
Read article →A writable update command list and an unsafe link handler affect System Manager. Inventory builds, inspect update and URI-launch traces, then upgrade.
Read article →CISA added GitLab's CI regex code-execution flaw to its exploited list. Check self-managed versions, upgrade, and triage exposed servers.
Read article →Socket's campaign view connects blocked package installs and repository detections to the scans and Firewall events behind them.
Read article →Cisco identifies affected products and one available fixed release while investigating major network platforms after four Node.js flaws.
Read article →Showing 27–39 of 145