StepSecurity Maps Agent Plugins Across Developer Machines and Repositories
A new two-sided inventory links Claude Code and Codex plugin installations to repository publishers, enablement, components and observed source.
Read article →AI systems, model security, agent abuse, and attacks that use generative tools.
A new two-sided inventory links Claude Code and Codex plugin installations to repository publishers, enablement, components and observed source.
Read article →Huntress traced fast retries, a scripted tenant sweep and requests that continued after a Teams principal was deleted. Check app credentials as well as sign-ins.
Read article →The 1.107.0 image provenance named a hyphenated source owner; startup files in that revision matched a poisoned PyPI wheel. Compare release inputs with shipped bytes.
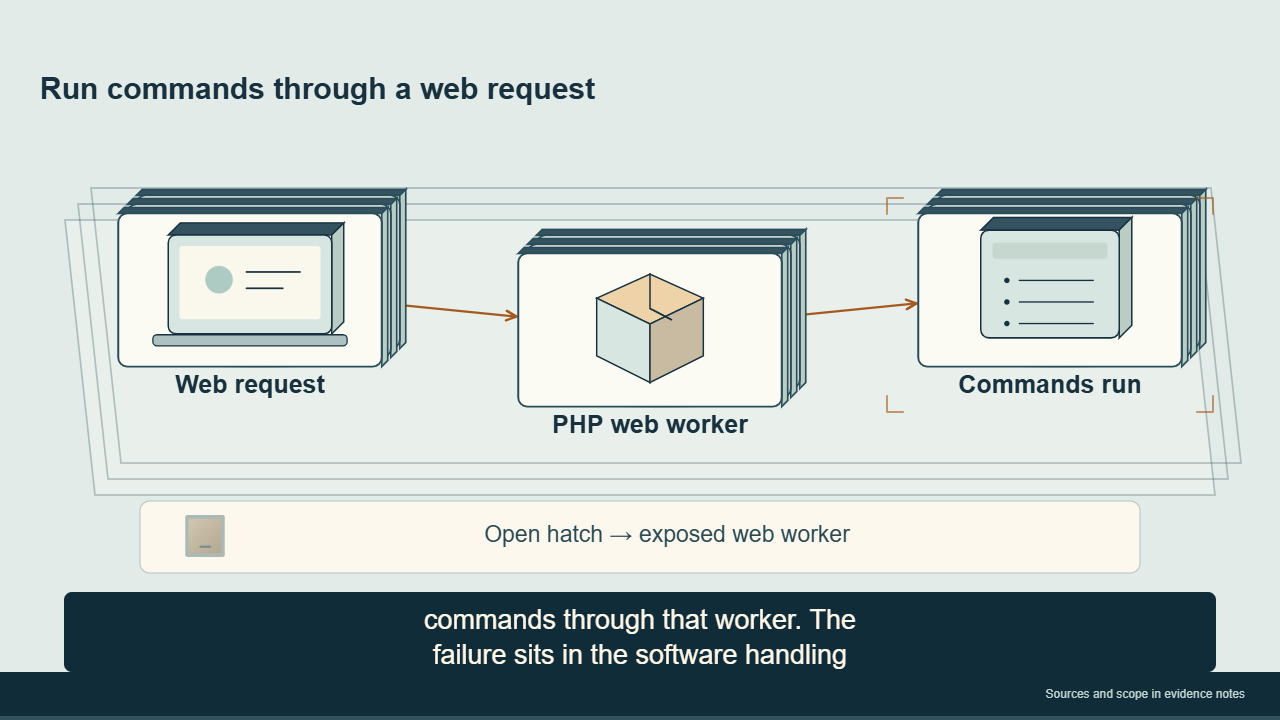
Read article →Unit 42 observed access to password hashes and MFA secrets after PHP exploitation. Patch the serving workers, then hunt their child processes and investigate credential access.
Read article →Two short-lived GitHub Actions branches reached organization and environment secrets before the poisoned LiteLLM release. Hunt the run and deployment records, then rotate exposed credentials.
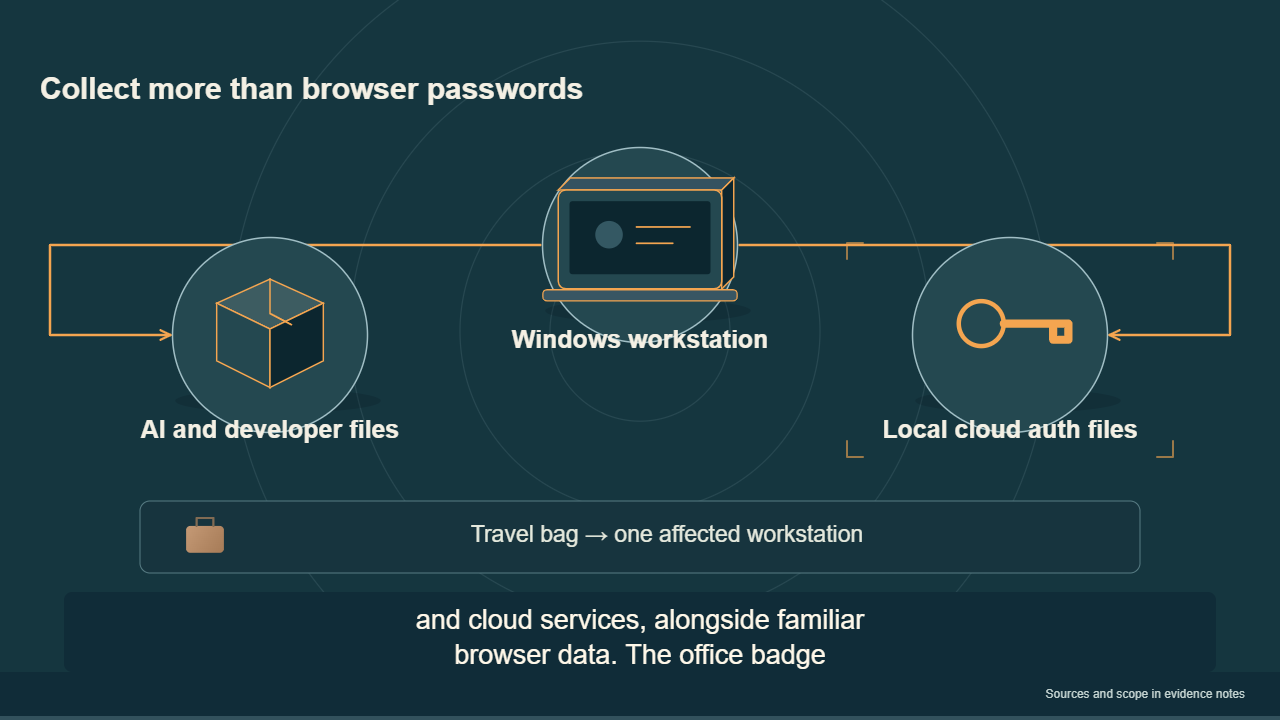
Read article →Check Point maps local AI-tool sessions, Git and cloud secrets to a Windows stealer; a host match calls for credential rotation from a clean machine.
Read article →Python startup hooks in LiteLLM 1.107.0 wheels and container images collected secrets and launched a second, hourly code loader. Trace image digests, rebuild and rotate reachable keys.
Read article →An AI-assisted actor stole more than 5,200 university records after accessing a weakly protected database. Trace WordPress login attempts and database exports separately.
Read article →New agent identity and risk-responsive controls target a familiar failure: an assistant inherits more authority than its current job needs. Start at the tool-call boundary.
Read article →Endpoint AI can flag unusual access, but a familiar-looking transfer may still be harmful. Put explicit policy at the upload and measure the review queue.
Read article →The joint guidance separates model evaluations from the permissions, data access and tools of the application that uses a model.
Read article →A replayed Chrome-to-Windows intrusion left encoded script in free memory. Capture RAM early, then use host artifacts to guide wider collection.
Read article →Attackers changed PHP configuration to reload a web shell, stole passwords through a sudo alias and searched government mailboxes for social media access.
Read article →Showing 27–39 of 82