Zimbra Exploit Tests Produce False Negatives on Vulnerable Servers
Elastic reproduced the SMTP-to-shell path and found public tests that miss the Swatchdog trigger. Check the SNMP setup, installed release and process lineage.
Read article →Threat actors, malware campaigns, phishing, exploitation, and incident activity.
Elastic reproduced the SMTP-to-shell path and found public tests that miss the Swatchdog trigger. Check the SNMP setup, installed release and process lineage.
Read article →Gheist plants short-lived Actions runs on attacker branches. Hunt deleted runs and cloud role assumptions, then rotate secrets exposed to affected repositories.
Read article →Quest believes someone accessed patient records in its Quanum LSM ordering and results system. Clients should identify their use of the service and request incident-specific scope.
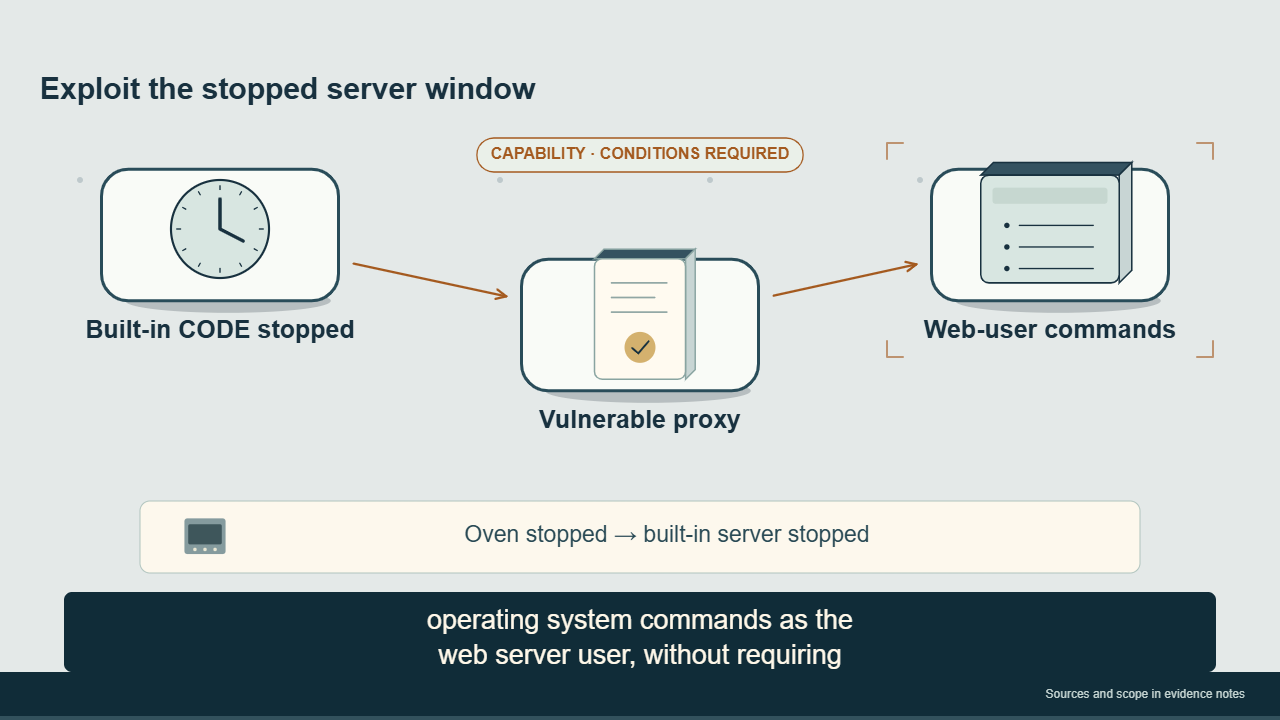
Read article →The richdocumentscode proxy exposes command execution while its CODE server is down. Update to 26.4.303 or remove the app, then look for web shells.
Read article →Two short-lived GitHub Actions branches reached organization and environment secrets before the poisoned LiteLLM release. Hunt the run and deployment records, then rotate exposed credentials.
Read article →GlobalProtect bypass reached vCenter in one Unit 42 case. Find successful gateway sessions, check cookie settings and update every cookie-using portal and gateway.
Read article →Python startup hooks in LiteLLM 1.107.0 wheels and container images collected secrets and launched a second, hourly code loader. Trace image digests, rebuild and rotate reachable keys.
Read article →An AI-assisted actor stole more than 5,200 university records after accessing a weakly protected database. Trace WordPress login attempts and database exports separately.
Read article →Two PHP flaws rated 9.2 leaked before fixes. Locate PHP in exposed sites and bundled software, watch worker child processes, and prepare for the vendor release.
Read article →Attackers chain four Plex flaws to run code on unpatched servers. Check the installed build, investigate Plex child processes and Codecs files, and rebuild compromised hosts.
Read article →A third of the KEV entries Talos analyzed trace to pre-2026 CVEs. Check whether your inventory keeps long CVE IDs and CISA's forensic-triage flag.
Read article →A stolen recovery code led to a registered Entra device, SharePoint downloads and a ServiceNow user export. Trace the session across each federated app.
Read article →Cisco Talos traces four delivery routes across nine countries. Hunt Startup-folder changes and unexpected PowerShell, then update affected Windows archive tools.
Read article →Showing 53–65 of 220