Cisco ASA and FTD VPN Flaw Lets Attackers Reload Firewalls
Cisco reports active exploitation of a remote-access VPN flaw. Check secondary authentication on exposed tunnel groups and move ASA and FTD to fixed releases.
Read article →Network activity, protocols, infrastructure, and detection.
Cisco reports active exploitation of a remote-access VPN flaw. Check secondary authentication on exposed tunnel groups and move ASA and FTD to fixed releases.
Read article →Talos traced an exploited peering-authentication bypass to a controller implant that reads decrypted control traffic. Compare peering events and authentication logs before upgrading.
Read article →An exploited Linux page-cache flaw is on CISA’s KEV list. Local users can reach the ESP decryption path; compare running kernels with fixed branch releases and investigate suspect hosts.
Read article →Attackers are targeting exposed PAN-OS management interfaces. Restrict web UI and XML API access, then match each installed build to its hotfix.
Read article →A short TCP message can make older vsomeip endpoints allocate gigabytes. Upgrade to 3.7.4 or set a reliable message-size limit, then check memory and connection logs.
Read article →Elastic reproduced the SMTP-to-shell path and found public tests that miss the Swatchdog trigger. Check the SNMP setup, installed release and process lineage.
Read article →Affected firewalls need Brotli inspection and dataplane TLS decryption. Check the setting, disable inspection while hotfixes are pending, and verify the result.
Read article →FortiOS remains under investigation. Node.js has patched Brotli memory corruption and nine other flaws in the 22.x, 24.x and 26.x lines.
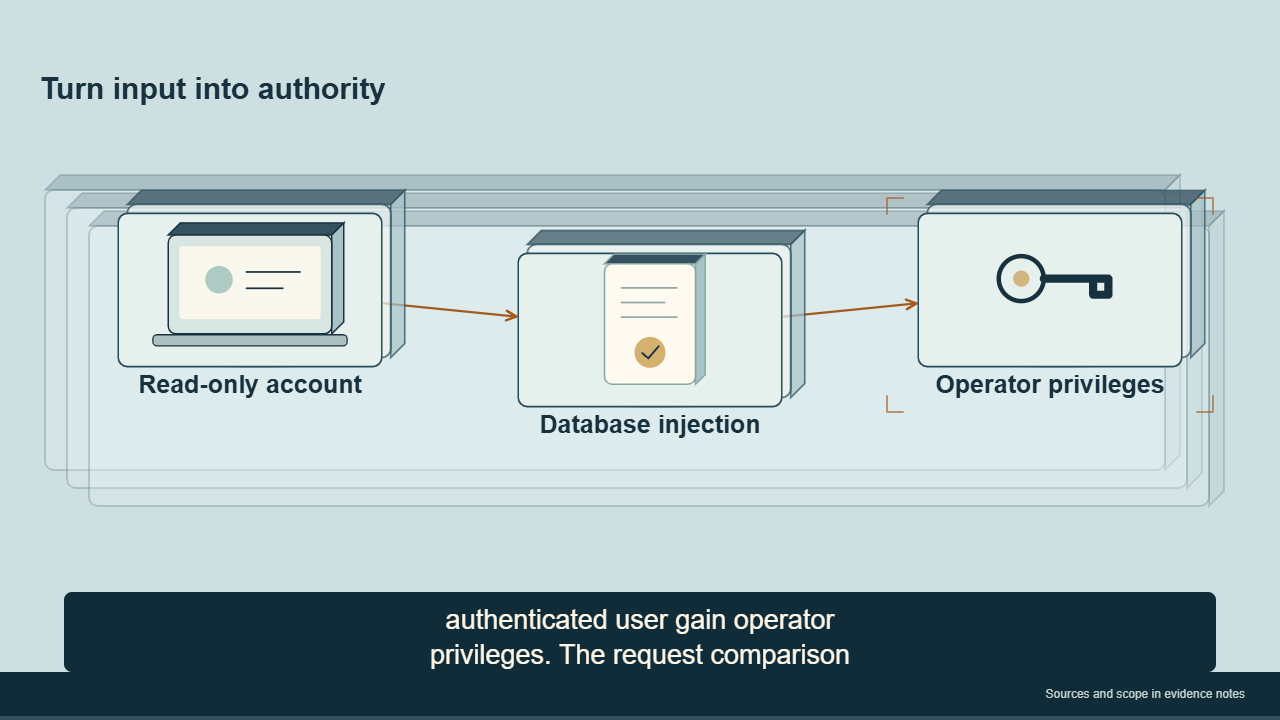
Read article →CISA lists the on-prem VCO flaw as exploited. An authenticated tenant reader can reach operator privileges; compare your release with Arista's fixed builds.
Read article →Cisco names Expressway and URWB as affected by the PHP2shell flaws, with product releases still ahead. Sort deployed products by advisory status and protect administrator access.
Read article →GlobalProtect bypass reached vCenter in one Unit 42 case. Find successful gateway sessions, check cookie settings and update every cookie-using portal and gateway.
Read article →A persistent database cookie and unchecked cluster client certificates put clustered Expressway-C and Expressway-E devices at risk. Move affected releases to X15.5.20.
Read article →Eight eMudhra intermediate keys were recoverable. Browser blocks cover six TLS keys; check separately managed trust paths and rebuild Go services with fixed releases.
Read article →Showing 27–39 of 109