Cisco Talos Traces Quick Assist Call Into VYPR Ransomware
A vishing call opened a Quick Assist session in a Talos case. The intruder moved through existing remote-management software, stole data and disabled endpoint defenses.
Read article →Authentication, access, credentials, and identity systems.
A vishing call opened a Quick Assist session in a Talos case. The intruder moved through existing remote-management software, stole data and disabled endpoint defenses.
Read article →Mandiant saw ARTEX compress permission checks into seconds and leave noisy application traces. Scope credentials and restrict management paths before the next burst.
Read article →Operators supplied access and objectives; agents then pursued credentials, domain privileges and shared files. Check AD activity and isolate backups.
Read article →Binance described a possible laptop-to-container path; examine who could submit withdrawal requests to signing systems.
Read article →Talos traced a Windows stealer that uses stolen sessions to check delivery receipts, then sends a victim profile to OpenRouter for assessment.
Read article →Three removed add-ons copied Phantom, Jupiter and Bitget; one also fetched code after review. Check extension IDs and move exposed wallet funds to a new seed.
Read article →Two intrusions began with remote-support impersonation; one reached DCSync and file-server theft after an identity containment exclusion.
Read article →Network access to vCenter can bypass authentication or lead to code execution; VM administrators can reach an ESXi host through VMXNET3. Match each branch to Broadcom's fixes.
Read article →With a known chain code, a compromised leaf signer share can lead back to the same party’s root share. Keep chain codes confidential while a library fix is pending.
Read article →Huntress traced fast retries, a scripted tenant sweep and requests that continued after a Teams principal was deleted. Check app credentials as well as sign-ins.
Read article →Gheist plants short-lived Actions runs on attacker branches. Hunt deleted runs and cloud role assumptions, then rotate secrets exposed to affected repositories.
Read article →Sophos traced app-only Graph token requests through consenting tenants, including those without active backups. Check old SkyKick consent and service-principal sign-ins.
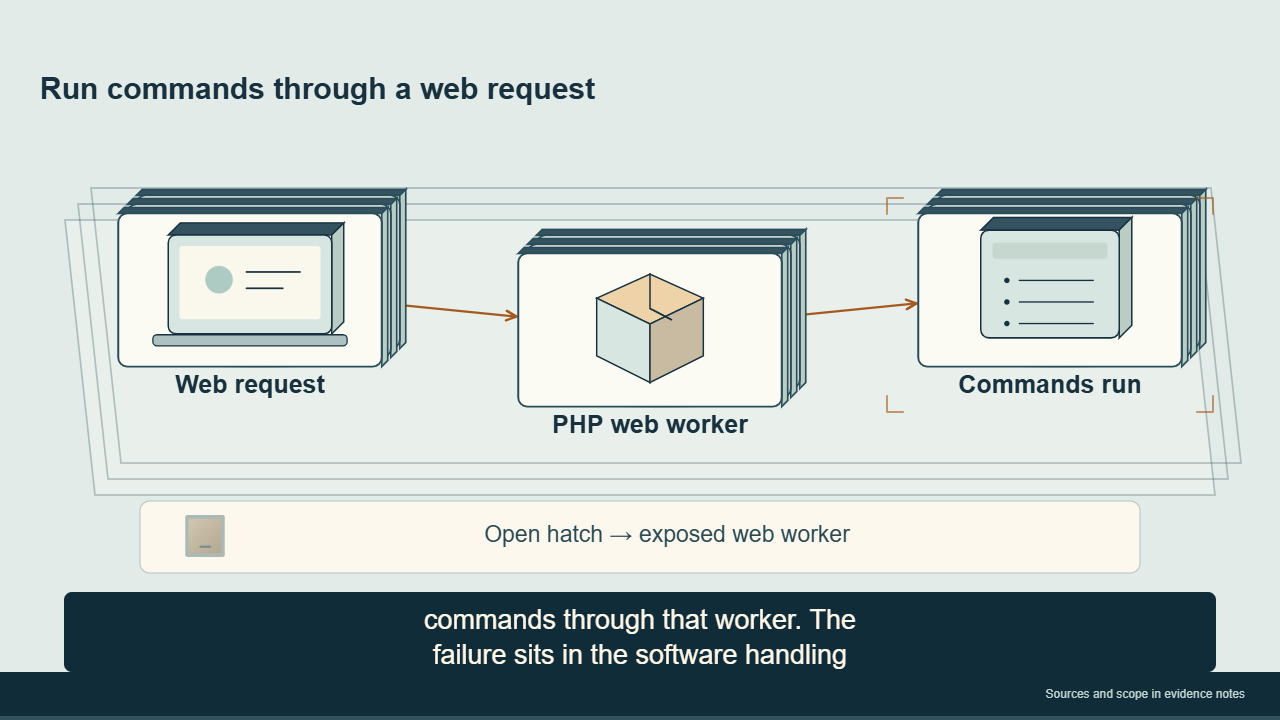
Read article →Unit 42 observed access to password hashes and MFA secrets after PHP exploitation. Patch the serving workers, then hunt their child processes and investigate credential access.
Read article →Showing 27–39 of 112